

Board Cybersecurity Briefing Template That Drives Action
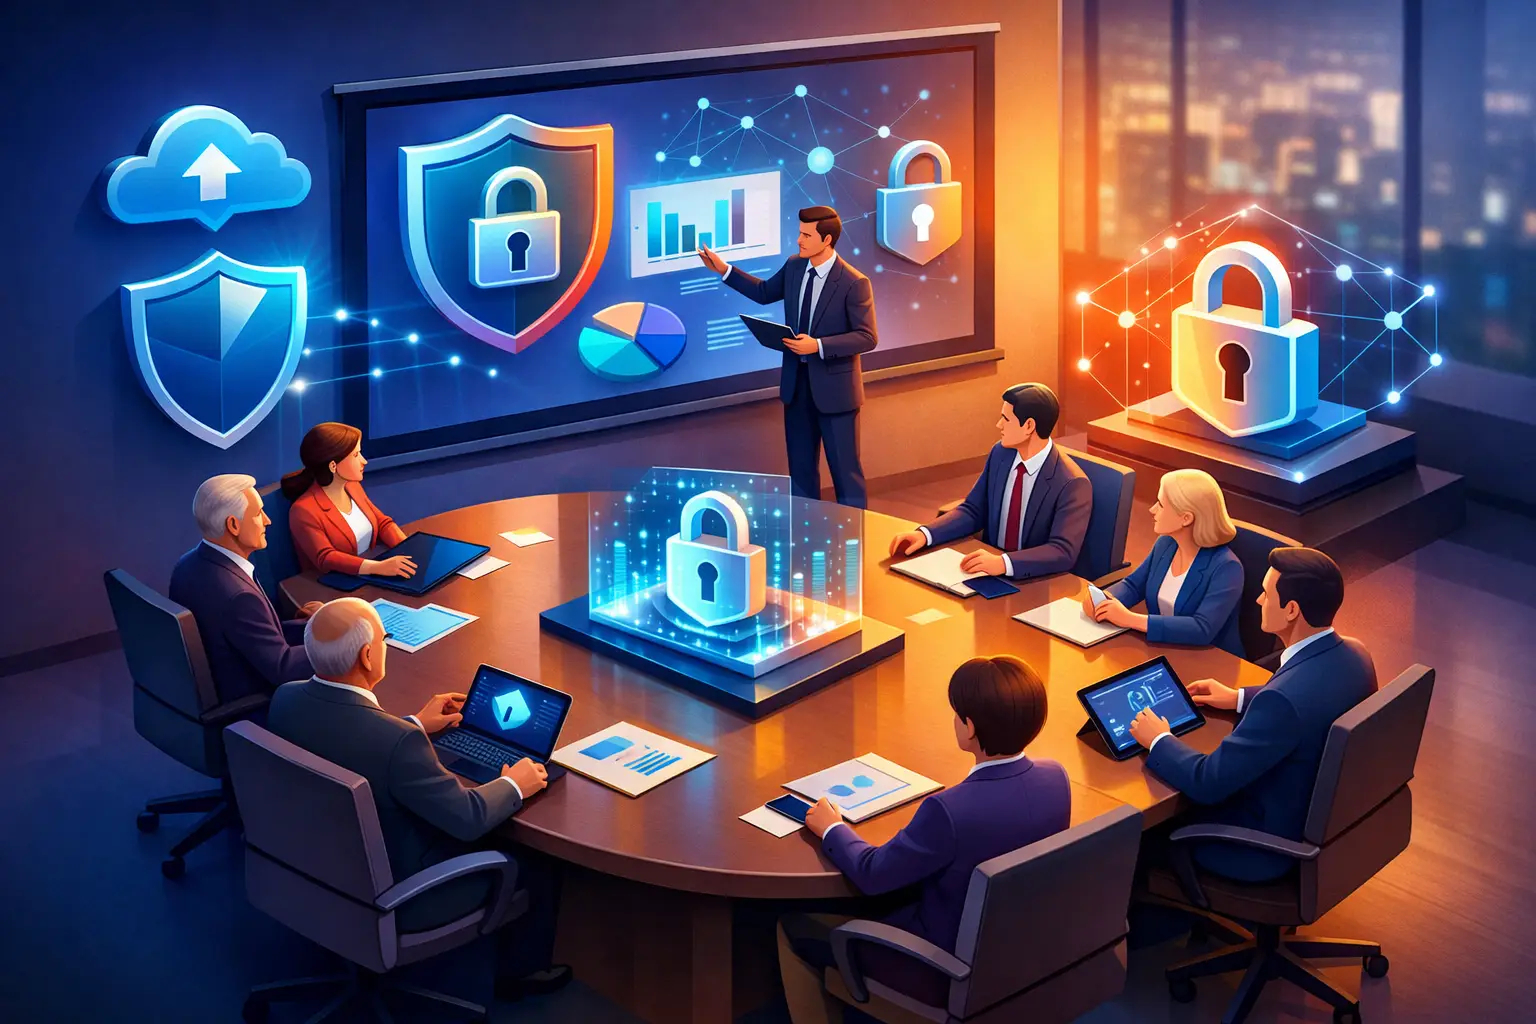
A board cybersecurity briefing template is not a reporting exercise. It is the mechanism that turns cyber risk into a business decision: what could disrupt revenue, expose regulated data, stop operations, or create personal accountability for leadership. If the board leaves a briefing with more technical terms but no clearer decisions, the briefing failed.
Boards do not need a tour of security tools. They need a clear view of material risk, the organization’s readiness, the decisions required, and the consequences of delay. The CISO’s job is to make that view credible without reducing a complex threat landscape to a misleading green, yellow, or red dashboard.
What a Board Cybersecurity Briefing Must Accomplish
A useful briefing answers five questions before board members have to ask them. What has changed since the last meeting? What is the organization’s most significant cyber exposure? How prepared are we to prevent, detect, and recover? Where does management need board direction or investment? And how will leaders know whether the risk position is improving?
This framing matters because security teams and boards operate at different altitudes. Security teams work through vulnerabilities, log sources, identity controls, vendor configurations, and incident playbooks. The board governs enterprise risk, capital allocation, regulatory exposure, operational continuity, and executive accountability. Both perspectives are necessary. Neither is sufficient on its own.
The right briefing creates a common language. A critical vulnerability is not just a technical finding. It may be an unpatched path into systems that process customer payments. A failed phishing simulation is not simply a training metric. It may indicate that a business unit is more likely to initiate the fraud or ransomware event that interrupts operations.
The Board Cybersecurity Briefing Template
Use the following structure for a quarterly board update, with a shorter version for regular committee meetings. Keep the core briefing focused enough to be read in advance and discussed in the room. Detailed technical evidence belongs in an appendix available to directors who need it.
1. Start with the executive risk statement
Open with a short, direct assessment of the current risk posture. State whether overall cyber risk is within the organization’s agreed tolerance and explain the primary reasons. Avoid vague statements such as risk remains elevated. Nearly every organization faces elevated risk. Explain what is materially elevated for this business.
For example, a meaningful statement might say that the organization’s exposure to business email compromise has increased because of a recent finance-system change, incomplete multifactor authentication coverage for external contractors, and a rise in targeted impersonation attempts against payment approvers. The business implication is potential fraudulent payment, delayed supplier operations, and reporting obligations.
This section should also identify the one to three risks that deserve board attention now. More than that often signals that management has not prioritized the issue.
2. Show material changes since the last briefing
Boards need movement, not a static inventory. Identify changes in the threat environment, the business environment, and the control environment. A new acquisition, expansion into a regulated market, migration to cloud services, critical supplier issue, or major workforce change can alter risk faster than any individual malware campaign.
Be explicit about positive progress as well. If endpoint coverage rose, recovery testing improved, or privileged access was reduced, explain why that lowers exposure. Progress should be tied to a risk scenario, not presented as a list of completed projects.
A useful format is to describe each change in three parts: what changed, why it matters to the business, and what management is doing next. This gives directors enough context to challenge assumptions without forcing them into technical detail.
3. Report readiness against real business scenarios
Maturity scores can be helpful, but they rarely tell a board whether the organization can withstand a damaging event. Scenario-based reporting is clearer. Select the scenarios most relevant to the organization, such as ransomware affecting a core platform, payment fraud through email compromise, compromise of a key supplier, theft of sensitive customer data, or disruption of industrial and operational technology.
For each scenario, show prevention, detection, response, and recovery readiness. The point is not to claim perfect readiness. It is to identify where a control gap would affect the organization’s ability to continue operating.
A ransomware scenario, for instance, should address whether critical systems are segmented, whether backups are isolated and tested, how long restoration would take, who can authorize business shutdowns, and whether crisis communications are prepared. A board can understand those questions because they relate directly to downtime, customer commitments, revenue, and leadership decisions.
4. Translate metrics into evidence of risk reduction
Metrics earn a place in a board pack only when they support a decision or validate a risk claim. Reporting the number of blocked attacks may sound impressive, but it rarely reveals whether the business is safer. Focus instead on leading and outcome-oriented measures.
Useful measures may include coverage of multifactor authentication for high-risk access, time to contain high-severity incidents, recovery performance against established objectives, critical supplier assessments completed, remediation of internet-facing critical exposures, and workforce reporting rates for suspicious messages. Training completion alone is not enough. The more meaningful question is whether people can recognize, report, and avoid behavior that creates measurable exposure.
Context is essential. A lower phishing failure rate may indicate improvement, but it can also reflect an easier simulation. A shorter remediation time may look positive while the number of high-risk assets grows. Trend data, targets, and clear ownership help directors interpret the number correctly.
5. State decisions, investment, and accountability clearly
Do not make the board hunt for the ask. If management needs approval for a recovery program, increased security staffing, a change in risk tolerance, or a decision to accept a known exposure, state it plainly.
Every request should include the decision required, the risk addressed, the expected outcome, the cost, the accountable executive, and the consequence of not acting. This is where cybersecurity becomes governable. A request for additional identity controls is stronger when it is presented as a way to reduce the likelihood of account takeover across high-value business systems, with defined implementation milestones and named ownership.
There are legitimate trade-offs. A fast acquisition integration may require a temporary risk acceptance. A legacy system may be too costly to replace immediately. The board does not need management to pretend these choices are easy. It needs management to present the options, residual risk, timeline, and controls that will limit exposure in the meantime.
Design the Briefing for Discussion, Not Decoration
A polished dashboard can hide weak governance. Each slide or page should be able to withstand a direct question: What does this mean for the business, how do we know, and who owns the next action?
Limit technical acronyms, especially when they do not change the decision. Define the few terms that are necessary. Avoid using compliance status as a substitute for security performance. Meeting a framework requirement can demonstrate discipline, but compliance does not guarantee resilience against a fast-moving attack. The reverse is also true: a capable security program can still create regulatory exposure if its evidence, documentation, and governance processes are weak.
For organizations subject to NIS2 or similar resilience requirements, board reporting should show how governance, incident readiness, supply chain risk, and workforce education connect. Directors should be able to see not only whether a policy exists, but whether the organization can demonstrate training, testing, escalation, and accountability when regulators or customers ask.
Build a Reliable Reporting Process
The quality of the briefing depends on the process behind it. Establish metric definitions, data owners, thresholds, and review dates before reporting season begins. If different teams calculate the same measure differently, the board will lose confidence quickly.
The CISO should work with legal, privacy, finance, operations, HR, and internal audit where relevant. Cyber risk crosses every one of those functions. HR and learning teams, for example, can provide evidence that awareness education reaches the right roles, reinforces high-risk behaviors, and creates measurable improvement rather than a check-the-box completion rate.
Run a pre-brief with the CEO, general counsel, or risk leader when the issue is material. This does not mean softening the message. It means ensuring leadership understands the risk statement, agrees on the facts, and is prepared to make decisions in the meeting.
Finally, preserve a record of board questions, decisions, and accepted risks. Those records improve follow-through and demonstrate that cyber governance is active, not ceremonial.
Cybersecurity starts with people, decisions, and disciplined execution - not a longer slide deck. Give your board a briefing that makes the next decision clearer, assigns ownership before the meeting ends, and proves that risk reduction is being managed with the same rigor as every other critical business priority.
FAQ
1. What must a board cybersecurity briefing accomplish?
Provide a clear view of material risk, readiness, required decisions, and consequences of delay.
2. Why shouldn’t boards receive technical tours?
Because boards govern enterprise risk, capital, regulation, continuity, not logs or configurations.
3. What is an executive risk statement?
A concise declaration of risk posture and 1–3 exposures requiring immediate board attention.
4. What counts as “material changes”?
Threat shifts, business changes, cloud moves, supplier issues, workforce changes — with why it matters.
5. Why use scenario‑based reporting?
Because it shows whether the organization can prevent, detect, respond, recover from real events.

Written by: Ivan Energiev
IT Project Coordinator · Operations Excellence & Service Delivery Leader at Advanced Vision IT Ltd | Published on September 24, 2026
Ivan advises insights on IT project coordination, operations excellence, and service delivery leadership.